


The emergence of Open Radio Access Network architectures has fundamentally changed the way telecommunications operators build and manage their infrastructure. By disaggregating hardware and software, Open RAN allows for a more diverse ecosystem of vendors and partners to contribute to the network. While this shift promotes innovation and reduces vendor lock-in, it also introduces significant new security challenges. The interconnections between different components and vendors create potential points of vulnerability that must be carefully managed. Implementing zero-trust data governance is essential in this environment to ensure that every interaction is verified and every piece of shared data is protected.
In a traditional closed network, security was often based on a perimeter model where everything inside the network was considered trusted. This is no longer viable in a collaborative ecosystem where multiple parties have access to various parts of the network infrastructure. Zero-trust data governance operates on the principle of never trust, always verify, meaning that every request for data access must be authenticated and authorized regardless of where it originates. This approach provides a much higher level of security by ensuring that even if one component is compromised, the rest of the network remains protected. For telecom operators, this means implementing granular controls over the telemetry and configuration data that is shared between different vendor systems.
Securing these interconnections also requires the use of standardized protocols and interfaces for data exchange. This ensures that all participants in the ecosystem are following the same security guidelines and that data can be tracked and audited as it moves between systems. By establishing a clear set of rules for how data is accessed and shared, operators can reduce the risk of unauthorized access and ensure that their network remains resilient in the face of evolving threats. This level of control is particularly important for 5G networks, where the high density of connected devices and the critical nature of the services provided make security a top priority.
Policy Enforcement in Distributed Industry Ecosystems
Modern telecommunications is increasingly becoming a collaborative effort that involves partnerships with cloud providers, content delivery networks, and specialized application developers. These distributed industry ecosystems rely on the exchange of large amounts of data to provide integrated services to end users. However, managing data governance across multiple organizations with different security standards and policies is a complex task. Zero-trust data governance provides a framework for consistent policy enforcement across these boundaries, ensuring that data is always handled in accordance with the owner’s requirements.
Central to this framework is the use of automated policy engines that can evaluate access requests in real time based on a wide range of factors. These factors include the identity of the user or system, the sensitivity of the data, the security posture of the requesting device, and the current threat environment. By using these dynamic policies, operators can ensure that data is only shared with authorized partners under the right conditions. This level of granularity allows for more secure collaboration without the need for static, broad-access agreements that can often be exploited by attackers.
Additionally, policy enforcement must be consistent regardless of whether the data is stored on-premises or in a public cloud environment. This requires a governance layer that can span different cloud platforms and provide a unified view of all data assets and access policies. By centralizing the definition of policies while decentralizing their enforcement, operators can maintain control over their data while still benefiting from the flexibility of distributed ecosystems. This approach is particularly effective when integrated with broader initiatives for data sovereignty compliance, as it allows for the enforcement of geographic restrictions alongside other security policies.
Verification Mechanisms for Continuous Access Control
One of the defining characteristics of zero-trust data governance is the shift from one-time authentication to continuous verification. In a traditional system, a user might log in once and then have access to various resources for the duration of their session. In a zero-trust model, the security system continuously monitors the activity and context of the user to ensure that they are still authorized to access the data. This provides a much higher level of protection against session hijacking and other forms of credential abuse that are common in sophisticated cyberattacks.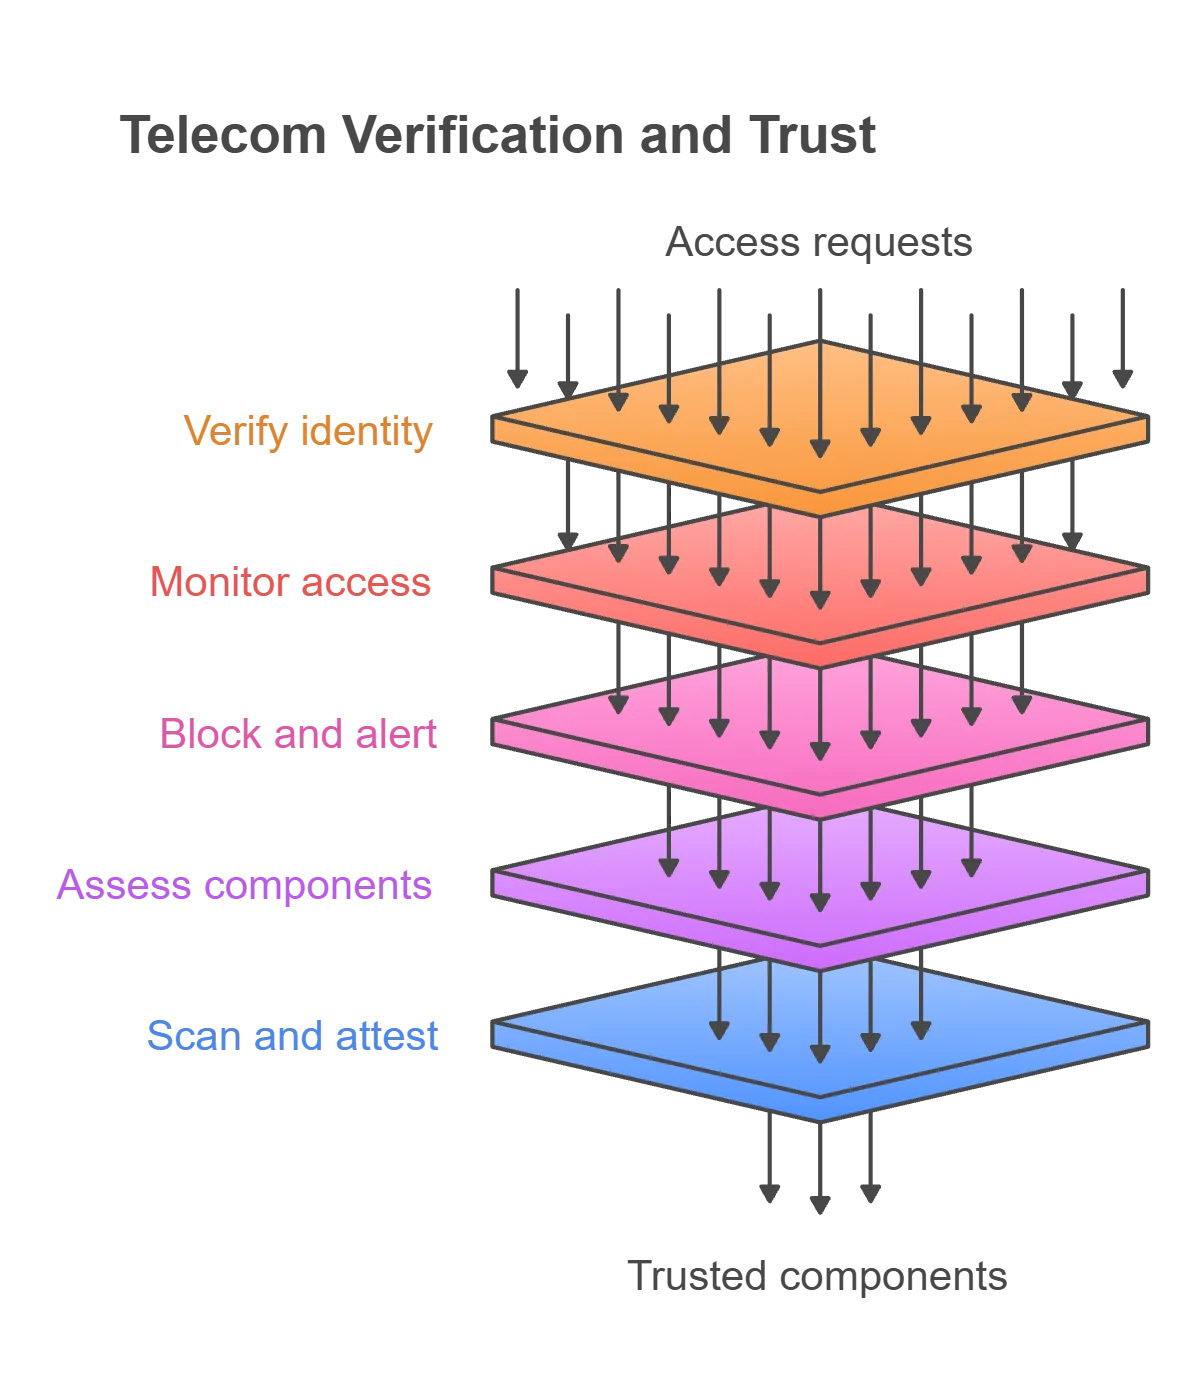
Verification mechanisms in a telecom context include the use of multi-factor authentication, biometric verification, and behavioral analytics. These tools provide multiple layers of assurance that the person or system requesting access is who they claim to be. Additionally, the system can monitor for unusual patterns of data access that might indicate a compromised account or a malicious insider. For example, if a network engineer suddenly attempts to download large volumes of subscriber records from an unusual location, the system can automatically block access and trigger an alert for further investigation.
Continuous verification also extends to the systems and applications that interact with the data. Every software component in a collaborative ecosystem must be regularly assessed for vulnerabilities and compliance with security standards. By using automated scanning and attestation tools, operators can ensure that only trusted and secure components are allowed to access sensitive network information. This level of scrutiny is essential for maintaining the integrity of the zero-trust framework and for preventing the spread of malware or other threats across the distributed network infrastructure.
Identity and Access Management for Collaborative Data
Effective identity and access management is the foundation of any zero-trust data governance strategy. In a collaborative ecosystem, this involves managing the identities of thousands of employees, partners, and automated systems across multiple organizations. This requires a resilient and scalable IAM system that can provide a single source of truth for all identities and their associated permissions. By using federated identity models, telecom operators can allow partners to use their own credentials while still maintaining control over what data they can access within the operator’s network.
Role-based access control and attribute-based access control are two common methods for managing permissions in a zero-trust environment. RBAC assigns permissions based on a user’s job function, while ABAC uses a more flexible approach that considers various attributes of the user, the resource, and the environment. In a complex telecom ecosystem, a combination of these methods is often used to provide the necessary level of control. For instance, a partner might have the role of a maintenance technician, but their access to specific network elements might also be restricted based on the time of day or their current physical location.
The use of modern IAM technologies also allows for more automated and efficient management of the identity lifecycle. This includes the automated onboarding and offboarding of users, as well as regular reviews of permissions to ensure that they are still appropriate. By reducing the reliance on manual processes, operators can minimize the risk of abandoned accounts or excessive permissions that can be exploited by attackers. A strong IAM system not only enhances security but also improves operational efficiency by making it easier for authorized users to access the data they need to do their jobs.
Mitigating Insider Threats and Third-Party Risks
Despite the focus on external attackers, insider threats and third-party risks remain significant concerns for telecommunications operators. Malicious or negligent employees, as well as compromised partner systems, can cause extensive damage if they have unrestricted access to sensitive data. Zero-trust data governance addresses these risks by limiting the potential for lateral movement within the network. By segmenting the network and implementing strict access controls between different zones, operators can ensure that a breach in one area does not automatically lead to the compromise of the entire system.
Data loss prevention tools also play a critical role in mitigating these risks. These tools can monitor for the unauthorized transfer of sensitive information and can automatically block transactions that violate security policies. In a collaborative environment, DLP must be applied not only to outgoing traffic but also to the data that is shared with partners and vendors. By ensuring that sensitive data is always encrypted and that access is strictly controlled, operators can significantly reduce the likelihood of a successful data exfiltration attempt.
Finally, regular audits and security assessments are essential for identifying and addressing potential vulnerabilities in the zero-trust framework. This includes not only technical scans but also reviews of governance policies and procedures. By maintaining a continuous cycle of monitoring, assessment, and improvement, telecom operators can ensure that their zero-trust data governance strategy remains effective against both internal and external threats. This proactive approach to security is essential for building a resilient and trustworthy organization that can thrive in an increasingly collaborative and connected industry.